
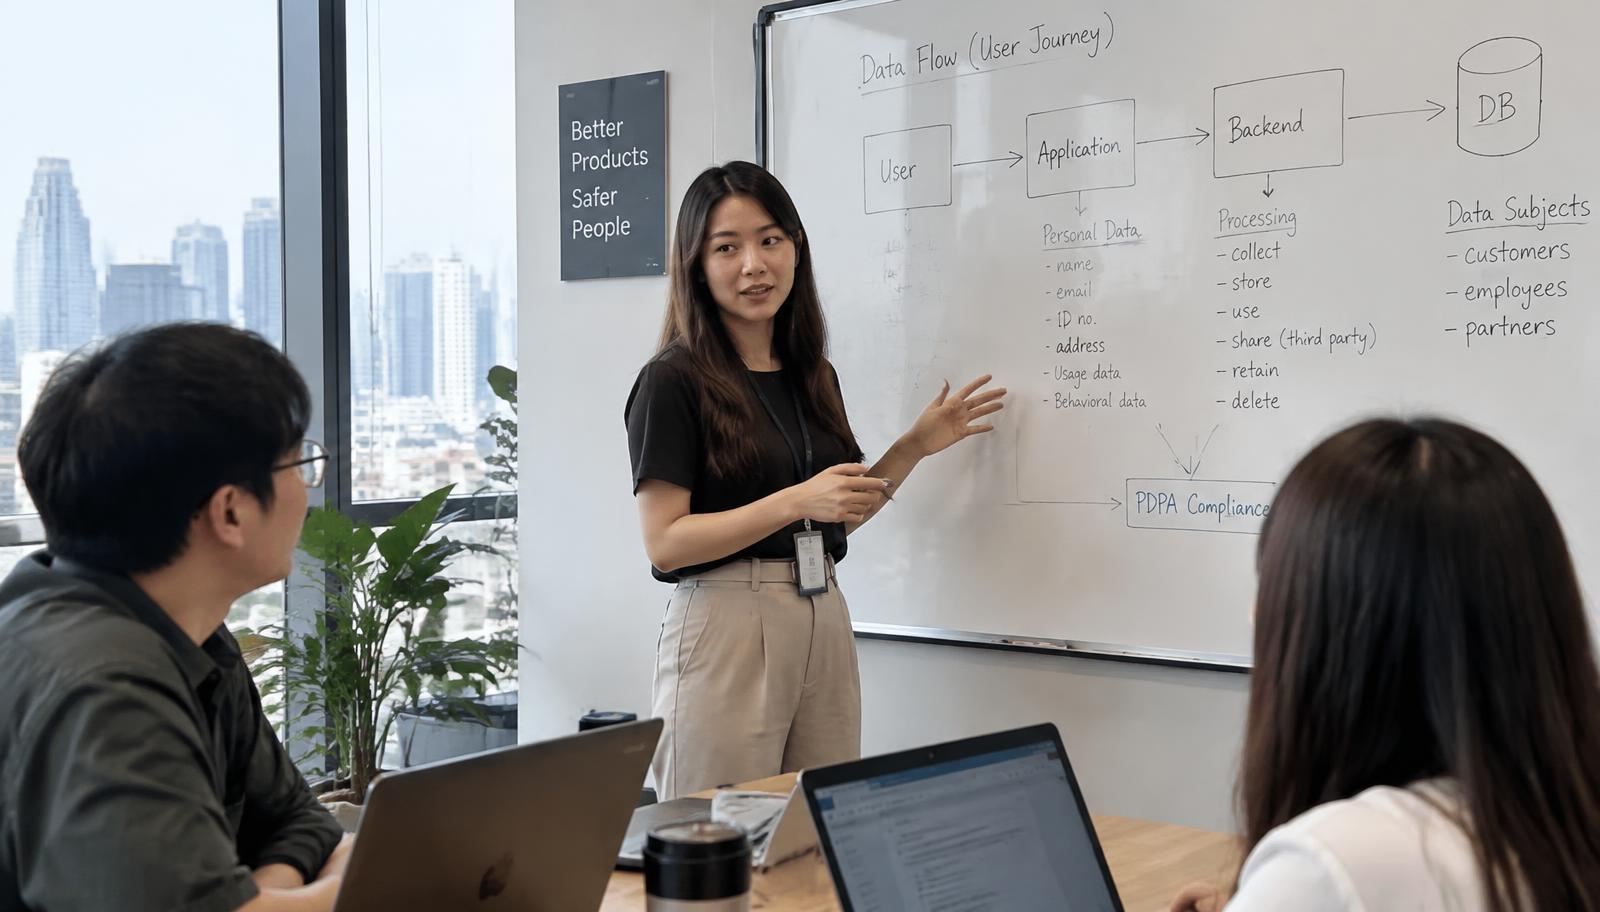
Thailand's Personal Data Protection Act B.E. 2562 (2019) has applied in full since 1 June 2022. Any business that collects personal data in Thailand — or targets people in Thailand from abroad — needs a lawful basis for each use, a privacy notice given at or before collection, a record of processing activities, reasonable security, a process for data subject requests, and a plan to notify the Personal Data Protection Committee office within 72 hours of becoming aware of a breach that is likely to put people at risk. A privacy policy page on its own is not compliance.
Last reviewed: 2026-10-04 · General information only, not legal advice for your specific case
Does the PDPA reach your business?
Most foreign managers first meet the PDPA when a Thai client sends a vendor questionnaire, or when a marketing team wants to launch a website with a contact form and tracking pixels. The Act is broader than either situation. It covers any controller or processor located in Thailand, whether or not the processing happens in Thailand. It also covers controllers and processors outside Thailand when they offer goods or services to people in Thailand, or monitor their behaviour while they are in Thailand.
That means a regional company that runs its Thai e-commerce store from Singapore, or a SaaS provider whose servers sit in Europe but whose sales team targets Thai customers, can fall under the Act. In those cases the law expects a representative in Thailand to be appointed in writing, subject to limited exceptions.
Personal data is defined widely: anything that can identify a living person directly or indirectly. Names, phone numbers, LINE IDs, email addresses, staff ID photos, CCTV footage, device identifiers and delivery addresses all count. Information about deceased persons and anonymised data that can no longer identify anyone fall outside the Act.
- Thai-registered company, including BOI-promoted and foreign-owned companies: in scope.
- Overseas company selling to or tracking people in Thailand: in scope, usually with a local representative.
- Personal or household use only: outside the Act.
- Sensitive data — health, biometrics, religion, criminal records, union membership, sexual behaviour, ethnicity, political opinions, disability and genetic data — needs explicit consent or another specific ground under Section 26.
Pick a lawful basis for each purpose, not one for the whole company
A frequent mistake is to treat consent as the default. The PDPA lists several grounds in Section 24: performing a contract, legal obligation, legitimate interest, vital interest, public task, research and archives, and consent. Consent is the weakest of these in practice because it can be withdrawn at any time and must be as easy to withdraw as to give.
Payroll processing, for example, rests on contract and legal obligations under labour, tax and social security law. Sending a newsletter to people who are not customers usually needs consent. Basic site analytics may rely on legitimate interest if the impact on visitors is low and they can object, while advertising cookies that build profiles across sites generally require consent.
| Activity | Typical lawful basis | Practical point |
|---|---|---|
| Employment records and payroll | Contract, legal obligation | Give an employee privacy notice at onboarding; keep tax and social security records for the legal retention period. |
| Customer orders and delivery | Contract | Collect only what fulfilment needs; delivery partners act as processors and need a data processing agreement. |
| Marketing email or LINE broadcasts to prospects | Consent | Use an unticked opt-in box and keep evidence of when and how consent was given. |
| CCTV in the office | Legitimate interest | Post notices at entrances and limit how long footage is kept. |
| Health checks or visa medicals for staff | Explicit consent or a Section 26 ground | Restrict access to HR and keep the records separate. |
The documents a credible programme needs
Regulators and corporate clients judge compliance by the paper trail as much as by the website. The set below is what we draft or review for most companies. The exact contents depend on what data you actually hold, so the work begins with a short data-mapping exercise rather than a template.
- Privacy notices for each audience: website visitors, customers, employees and job applicants. Each one states the purposes, lawful basis, retention period, recipients and the rights people can exercise.
- Record of processing activities (ROPA) under Section 39. Small businesses may be exempted by a PDPC notification for some processing, but the exemption does not cover sensitive data or high-risk processing.
- Cookie notice and consent tool that blocks non-essential cookies until the visitor agrees.
- Website Terms and Conditions covering use of the site, intellectual property, liability limits and governing law.
- Data processing agreements with vendors such as cloud providers, payroll bureaus, call centres and marketing agencies.
- Data subject request procedure, with a 30-day response target for access requests.
- Breach response plan naming who decides, who notifies the PDPC office and when affected people must also be told.
- Retention schedule and deletion routine.
How we build a PDPA programme
1. Data mapping workshop
We interview the people who actually handle data — HR, sales, IT, finance — and list each system, what it holds, who can see it and where it is sent.
2. Gap review
We compare the map with the Act and current PDPC notifications and rank the gaps by risk, so the most exposed processes are fixed first.
3. Drafting
Privacy notices, ROPA, website terms, cookie text and vendor agreements are written for your processes in Thai and English. Where the two language versions differ, we state which one prevails.
4. Website implementation
We work with your web team so the cookie banner really blocks tags before consent, forms link to the correct notice and consent records are stored.
5. Staff briefing and handover
A short training session for the teams that handle requests and incidents, plus a calendar for annual review.
Data breaches: the 72-hour clock
Section 37 requires a controller to notify the PDPC office without delay and, where feasible, within 72 hours after becoming aware of a breach, unless the breach is unlikely to result in a risk to people's rights and freedoms. If the risk is high, the affected individuals must also be told, along with the steps being taken to address it.
In practice the first day is lost working out what happened. A written plan that names the decision-maker, the external IT forensics contact and the person who files the notification turns a chaotic week into a manageable process. We recommend running a tabletop exercise once a year using a realistic scenario, such as a lost laptop or a misdirected payroll email.
When a Data Protection Officer is required
Section 41 requires a DPO when the core activities of the controller or processor involve regular and systematic monitoring of personal data on a large scale, or processing sensitive data as a core activity, or when the organisation is a public authority. A PDPC notification sets out what "large scale" means. A hospital, a large employer screening staff health data or a platform that profiles users would usually qualify; a small trading company typically would not.
The DPO can be an employee or an external service provider. They must be able to report to top management and must not be dismissed for performing DPO duties. Companies in a group may share one DPO if the person is easy to contact from each company.
Sending data outside Thailand
Regional groups often store HR and CRM data on servers in Singapore, the EU or the US. Sections 28 and 29 allow cross-border transfers when the destination has adequate protection, when binding corporate rules approved by the PDPC office are in place, when appropriate safeguards such as standard contractual clauses are used, or when specific exceptions apply, such as the data subject's informed consent or the performance of a contract.
We document the transfer route in the ROPA and add transfer clauses to intra-group and vendor agreements. That way the paperwork already exists when a Thai client's procurement team asks where its data goes.
Other digital laws that sit alongside the PDPA
- Electronic Transactions Act: electronic signatures and records are generally valid, which allows online terms and e-contracts to be enforced when properly presented to users.
- Royal Decree on digital platform services: certain platforms operating in Thailand must notify the Electronic Transactions Development Agency (ETDA).
- Computer Crime Act: obliges service providers to keep traffic data for a set period and penalises unauthorised access.
- Consumer protection rules: online sellers must disclose who they are and the main terms of sale.
Frequently asked questions
Is a privacy policy on our website enough?
No. It covers only one audience. Employees, job applicants and offline customers also need notices, and the Act expects internal records, security measures and request and breach procedures.
Do we need cookie consent in Thailand?
For non-essential cookies such as advertising and cross-site tracking, yes in practice. Strictly necessary cookies can run without consent, but they should still be disclosed in the cookie notice.
Our parent company is overseas. Can it use our Thai staff data?
Yes, if there is a lawful basis, staff are told in the employee notice, and the cross-border transfer meets Section 28 or 29, for example through intra-group agreements with appropriate safeguards.
Can you act as our DPO?
We can support a DPO function under a service agreement. Whether a DPO is legally required depends on your core activities, which we assess first.
Are the documents in Thai or English?
We usually prepare both. Notices for Thai staff and consumers should be in Thai so they are clearly understood. The English versions serve management and overseas group companies.
Official sources
Related services
Tell us what data you hold and where it goes
Send a short description of your systems, vendors and the audiences you collect data from. We will reply with the documents you need and the order to prepare them in.
Contact the team